Built for the most sensitive data you hold.
Encryption in transit and at rest, role-based access you control, and an audit log covering every action the agent takes.
Capabilities
The guardrails
Permission inheritance
The agent acts strictly within the permissions of the person who asked, never above them. A manager cannot reach another department's salary data by asking nicely.
Audit trail on every action
Each action is written to a log together with the instruction that caused it, so any change can be traced to a person and a request.
Held actions
Anything touching money, exits or compliance stops for explicit human approval regardless of who asked for it.
Encryption and access control
Data encrypted in transit and at rest, with role-based permissions you define per entity and per department.
In the product
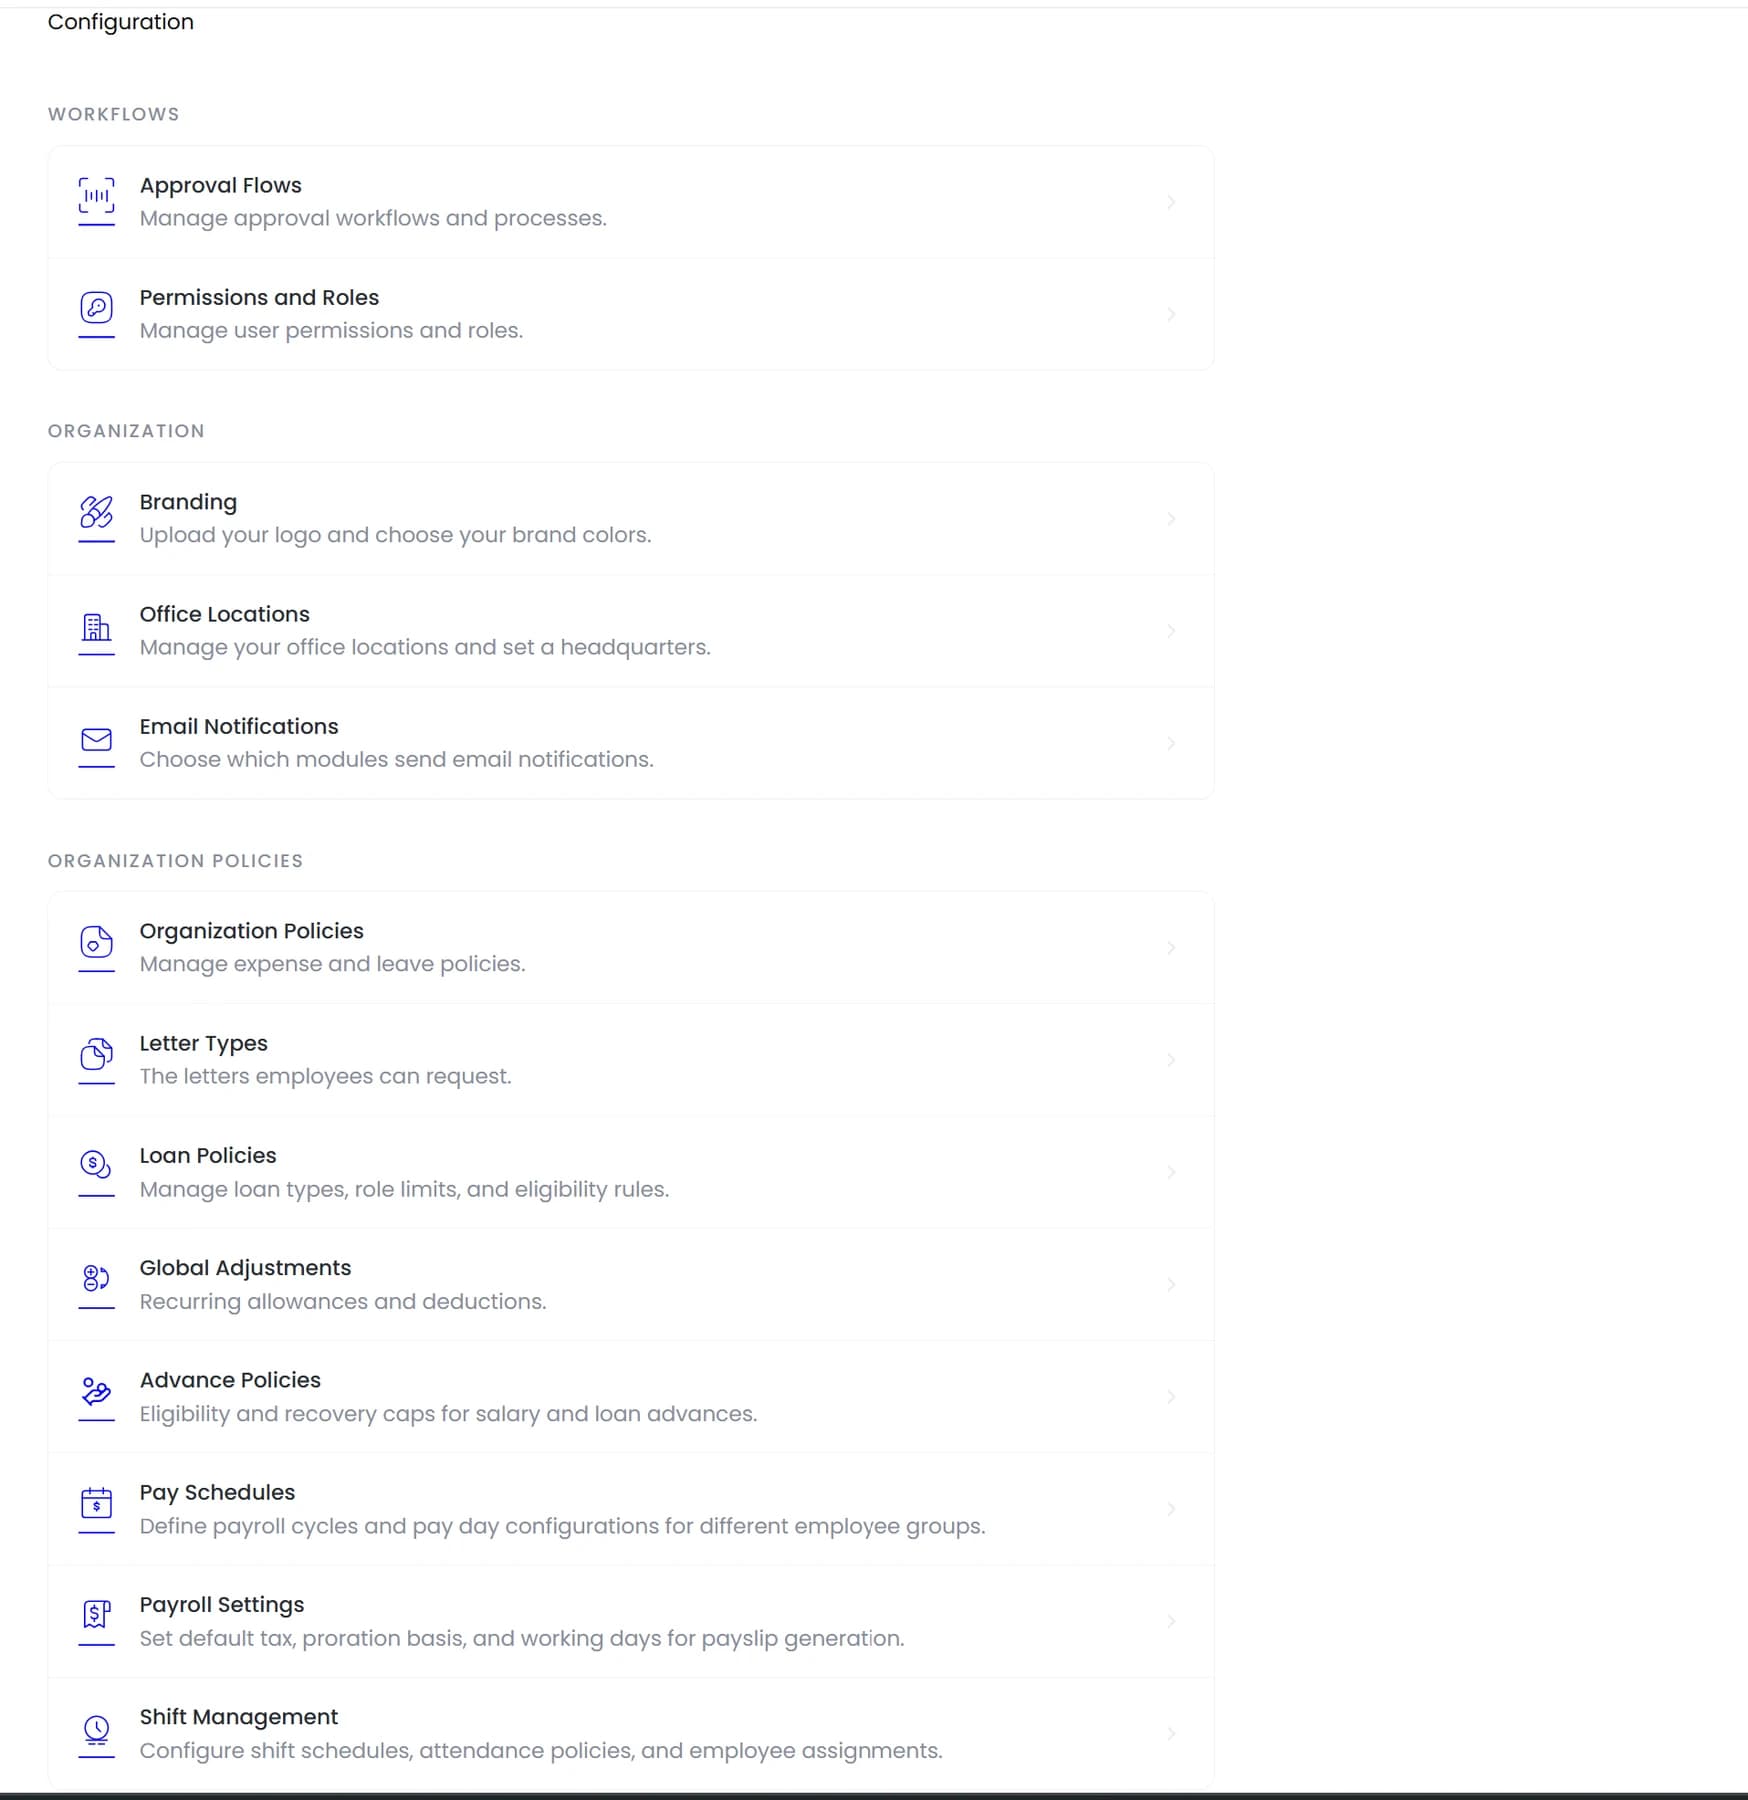
Approval flows, permissions and organisation policies configured in one place.
An agent operating on HR data is operating on the most sensitive dataset most companies hold. That makes the guardrails a product requirement rather than a footnote.
- Permission inheritance
- Audit trail on every action
- Held actions
- Encryption and access control
How it fits together
What an agent operating on HR data has to guarantee
An agent with access to payroll, contracts and personal records is operating on the most sensitive dataset most companies hold. That makes the guardrails a product requirement rather than a security footnote.
- Permission inheritance
- Audit trail
- Held actions
Security
The agent never acts above you
Three properties are non-negotiable, and they are worth demanding of any vendor you evaluate, not only this one.
By the numbers
What it looks like in practice
Terminations, pay decisions, grievance outcomes and probation calls are consequential and hard to reverse. The agent prepares and drafts. A person decides. That boundary is deliberate policy, not a current limitation.
Inherited
The agent never acts above you
Logged
Every action with its instruction
Held
Money, exits and compliance
Encrypted
In transit and at rest
In practice
How a request is authorised
The same checks apply whether a person clicks the button or asks Tio to do it.
Identity
Who is asking, established at login rather than inferred from the request.
Permission
Whether that person holds the permission for the action at all, checked against their current roles rather than a cached session.
Scope
How far the permission reaches. Self, team or organisation, which is what decides whether a manager sees one record or every record.
Reversibility
Whether the action can be undone. Anything touching money, exits or compliance is held for explicit human approval regardless of permission.
Record
The action and the instruction that caused it are written to the audit log, so it can be explained months later rather than merely observed.
Compared
Where the boundary sits
The split is about reversibility rather than difficulty.
FAQ
Common questions
Can we export the audit log?
Yes. It is available through the interface and the API, which matters when an auditor wants the evidence in their own format rather than a screen share.
Where is our data stored?
Data is encrypted in transit and at rest. Specific hosting regions can be confirmed for your jurisdiction as part of an evaluation.
Is customer data used to train models?
Your employee records are processed to answer your own questions. Confirm the current data processing terms as part of procurement, since this is exactly the clause worth reading rather than assuming.
See it running on your own data.
We will show the module working against records that look like yours, not a generic demo.
Explore more
Meet Tio
The agent that acts on your records rather than just answering questions.
Employee Records
Reporting lines, entities, locations and roles on one record that payroll, attendance, leave…
Integrations & API
Accounting, identity, communication and finance tools synced, so the agent always works with…